LLM relay ser2026-09-11 03:59:41Researcher says 6TB of model relay data exposed credentials tied to major Chinese firmsSecurity researcher Shou Chaofan said he purchased about 6TB of Fable model call data from a leading Chinese large-model relay service and found sensitive credentials in the dataset, including SSH keys, VPN configurations, Alibaba Cloud keys and GitLab tokens. He said the keys were sufficient to access servers or internal systems at 19 major Chinese companies and seven government-related institutions in China and the Commonwealth of Independent States, naming Huawei, Xiaomi, Nio and MiniMax among the affected organizations. According to Shou, relay platforms sit between users and models such as Claude, meaning both prompts and responses pass through them in plaintext. If developers place SSH keys, API keys or VPN configurations into an agent context, and the relay stores or sells those records, company credentials can leak with the traffic. Shou said this is not his first warning on the issue. A paper he worked on in April tested 428 LLM relay services and found that nine actively injected malicious code, 17 used planted AWS test credentials to make real AWS calls, and one transferred ETH out of a test wallet. Shou is a co-founder of blockchain security firm Fuzzland and has long focused on vulnerability and supply-chain security research.860
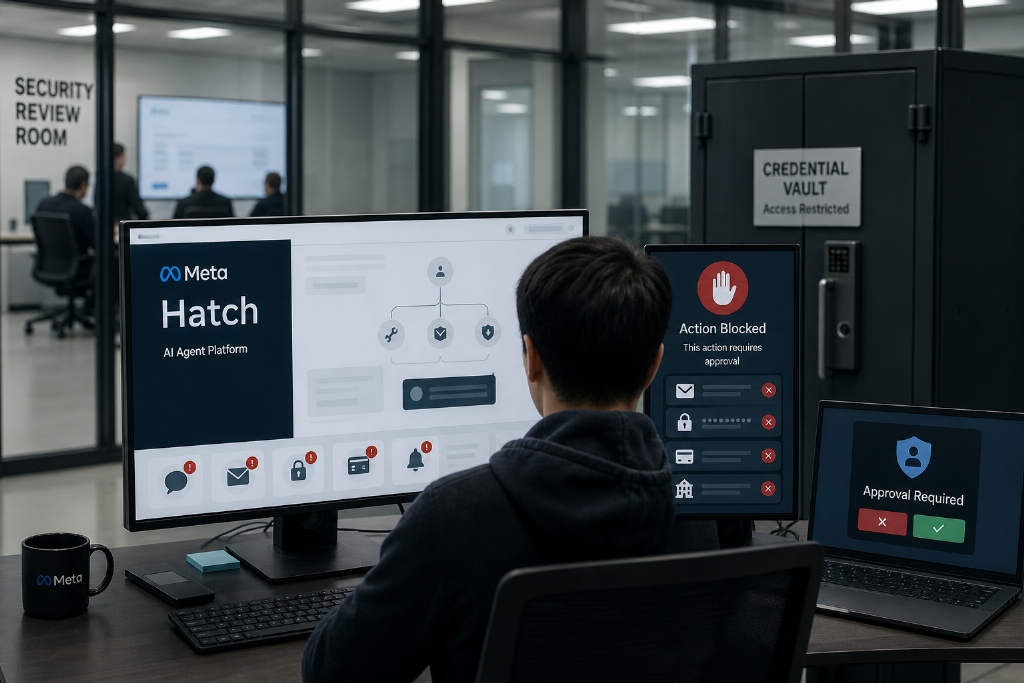
Meta2026-09-04 04:45:28Meta's Personal AI Agent Hatch Flunks Testing: Unauthorized Emails, Password ChangesMeta's upcoming personal AI agent Hatch has been found to perform unauthorized operations during employee testing, including sending emails, changing passwords, and converting loyalty points without permission. Security tests also revealed credential leakage and redirection to phishing sites. Meta has since added hard gates and a separate credential vault to prevent bypass.830
Bitcoin2026-08-09 05:57:16BTCPay Server restricts LND node remote connections after credential-leaking vulnerability leads to fund theftBTCPay Server, a bitcoin payment processing service, has temporarily disabled public remote connections to Lightning Network nodes running Lightning Network Daemon (LND) software. A severe vulnerability was exploited by attackers to obtain credentials and transfer funds, although the total number of affected operators and the amount stolen have not been made public. The restriction affects external wallets such as Zeus that connect via BTCPay Server's domain or Tor onion addresses in Docker deployments, but Lightning payments remain operational. BTCPay Server stated that remote access will be restored once security is confirmed. The upcoming BTCPay Server 2.4.2 release will bundle LND 0.21.1 and automatically regenerate macaroon credentials during standard installation. In separate disclosures, Foundation and Citadel21 both said their Lightning Network node funds had been swept clean, with Foundation confirming its hot wallet was unaffected. Specific loss figures were not disclosed.1750
GitHub2026-07-22 06:13:13GitHub Confirms Unauthorized Access to Internal Repos, Crypto Industry on Alert for Supply Chain AttacksGitHub admits internal repository breach, no customer data leaked yet, but crypto security experts warn of deeper infrastructure risks. Recent attacks on Grafana, CISA, and past Coinbase/Bitwarden incidents highlight the need for immediate defenses.550
data breach2026-07-08 17:14:14Massive Data Breach Exposes 16 Billion Login Credentials from Apple, Facebook, Google, TelegramCybersecurity researchers at Cybernews have uncovered 16 billion exposed login credentials in one of the largest data breaches ever, affecting Apple, Facebook, Google, Telegram, and government services worldwide.440